Authenticator App - SafeAuth

- 1.98K Reviews
- 4.4
- Downloads
- 10,000,000+
Our take on Authenticator App - SafeAuth from Appgk
Two-factor authentication is one of those protections that feels invisible until a login asks for a six-digit code at exactly the wrong moment. I tried to look at Authenticator App - SafeAuth as a practical daily tool rather than a flashy security product. Its job is simple: help protect online accounts with a second verification step, while adding PIN and biometric protection around the authenticator itself.
That simplicity is its biggest strength, but it also explains where people can become frustrated. An authenticator does not usually fix a blocked account, replace a password manager, or solve every login problem. It stores and generates verification codes, so the quality of the experience depends heavily on careful setup, a working phone, and keeping recovery information somewhere safe. When those pieces are in place, SafeAuth is an approachable choice for people who want stronger account security without depending on text messages.
Where SafeAuth users are most likely to get stuck
The first surprise for many new users is that installing the app does not automatically protect anything. Each account must be connected to the authenticator through that service’s own security settings. During that process, the account normally presents a QR code or a setup key, and the authenticator uses it to create the changing verification code. SafeAuth can be ready on the phone, yet still appear to do nothing until an account has been added properly.
I would therefore treat the first setup as a careful handoff rather than a quick tap-through. Keep the account’s setup screen open, add the entry in SafeAuth, and test the generated code before closing the account’s security page. A code that looks correct but is rejected is often a sign of a mistyped setup key, a scanned code that was not accepted cleanly, or a timing problem between the phone and the service.
Best Parts of Authenticator App - SafeAuth
Things to Keep in Mind About Authenticator App - SafeAuth
Another common point of confusion is the code’s short lifetime. A code nearing the end of its cycle may expire while it is being entered, especially if I switch between apps or pause to check another detail. In that situation, waiting for the next code and entering it promptly is more useful than repeatedly submitting the old one. This is a small habit, but it prevents a lot of unnecessary account-lockout anxiety.
SafeAuth’s PIN and biometric protection add a second layer around the code vault. That is valuable if someone can unlock the phone but should not automatically see every authentication entry. It also creates a responsibility: I need to remember the protection method I choose and keep the phone’s normal unlock process reliable. Security is only helpful when it remains usable during an actual login.
News and Features Related to Authenticator App - SafeAuth

News
YouTube Turns a Quick Video Check Into an Hour of Watching

News
BeautyPlus Makes Portrait Retouching Feel Like Your Own

News
TikTok’s Effortless Feed Makes Every Swipe Count—and Every Mistake Harder to Undo
The app is free to install, which makes it easy to try without committing money at the beginning. Its listing also shows optional in-app purchases ranging from a few dollars to more substantial individual items. I would not choose it on the assumption that every useful security function must be paid for; instead, I would review any purchase screen carefully and decide whether the added value matters to my own workflow.
What to check before blaming the code
When a verification code fails, I check the phone’s date, time, and time zone first. Authenticator codes are time-sensitive, so even a modest clock mismatch can make a perfectly generated code look invalid to the website. Turning on the phone’s automatic date and time settings is a sensible general fix, provided the device and network are behaving normally.
Don't want to read the full review?
I also check that I am using the entry for the correct account. Once several services are added, similar labels can make it easy to select the wrong line. A useful approach is to name entries clearly during setup, using the service and account identifier rather than a vague label such as “work” or “email.” That small organizational step becomes more valuable as the list grows.
On Android, SafeAuth supports devices running Android six or later. That makes it accessible to people using older phones, although I would still keep the operating system and the app current when updates are available through the normal store. The current version is 1.7.6, and staying current is a sensible maintenance habit for a security tool, even though an update alone cannot repair a wrongly configured account.
Screenshots
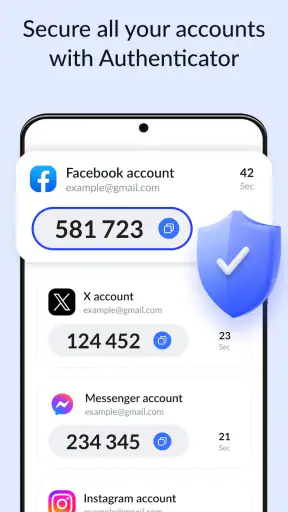
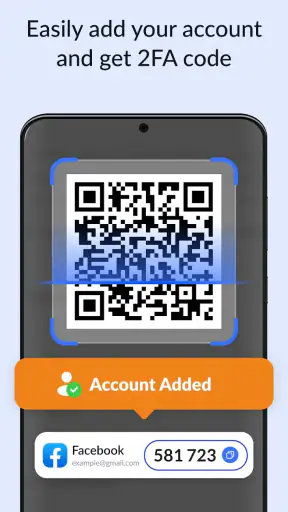
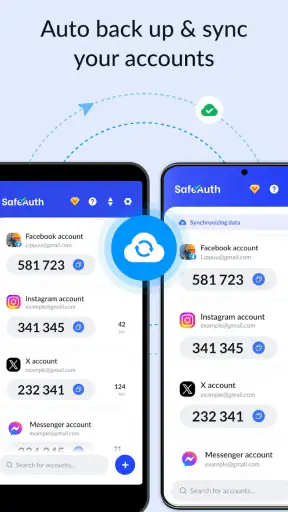
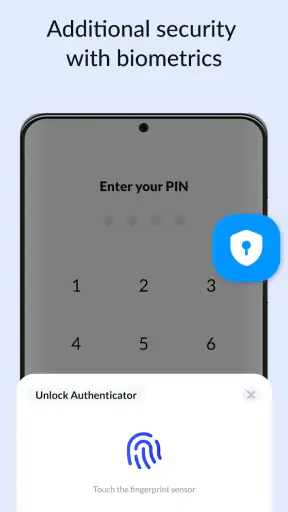
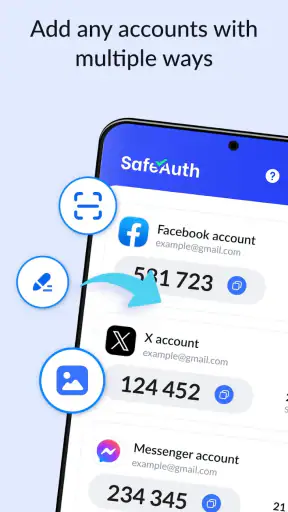
Before scanning a setup code, I make sure the camera is showing the entire code clearly and that the account’s security page has not timed out. If scanning is awkward, manually entering the setup key can be a useful alternative, but it demands careful attention to similar-looking characters. I would avoid guessing: one wrong character can create a code stream that never matches the account.
There is also a practical screen-management issue. If the account displays the QR code on the same phone where SafeAuth is installed, scanning becomes inconvenient or impossible unless the code is shown on another screen. In that case, using the manual key or opening the account setup on a computer is usually less frustrating. This is not a flaw unique to SafeAuth, but it is an important part of planning the setup.
A safer setup routine for important accounts
I would begin with a low-risk account before moving to banking, work, or a primary email account. That gives me a chance to understand the flow: open the account’s security settings, choose an authenticator method, connect SafeAuth, enter the current code, and complete a test sign-in. Once that process feels familiar, I can repeat it more confidently for accounts where a mistake would be costly.
The recovery step deserves as much attention as the code itself. Many online services provide backup codes or another recovery method when two-factor authentication is enabled. I would save those according to the service’s instructions in a secure place that is separate from the phone. The point is not to make the authenticator less important; it is to avoid being locked out if the phone is lost, damaged, reset, or unavailable.
I would not take a screenshot of a setup QR code and leave it in an ordinary photo gallery. The QR code or manual key may be enough to recreate the authenticator entry, so treating it like a password is the safer mindset. Once setup is complete, I would remove temporary copies from places that are easy for other people or apps to access.
SafeAuth’s own PIN or biometric lock is most useful when I configure it before adding many accounts. That way, the protection becomes part of the normal opening routine rather than an afterthought. I also prefer testing the lock while I am calm and signed in, rather than discovering a problem when I am rushing through an important login.
For a family member who is not comfortable with security settings, I would help create a written recovery plan without writing down active codes in plain sight. The plan could explain where the recovery codes are stored, which phone contains the authenticator, and who can help with account recovery. This is especially useful for accounts that are shared across household responsibilities, but the actual credentials should remain private.
SafeAuth is suitable for general audiences, and its content rating is Everyone. That does not mean setup is effortless for every age group. The difficult part is understanding account recovery and protecting the setup key, not pressing the buttons in the app. A short, supervised setup is better than handing someone an authenticator and assuming the security process is complete.
Recovering the workflow when something goes wrong
If a code is rejected, I avoid deleting the account entry immediately. First I verify the service name, check the phone clock, wait for a fresh code, and try again without switching between several login screens. Deleting an entry can remove a useful reference and may make recovery harder if I have not retained the original setup key or backup method.
If the phone has been replaced, the recovery path depends on the account rather than on the authenticator alone. I would use the service’s backup codes, a previously configured recovery method, or its official account-recovery process. After regaining access, I would register the new phone and test it before removing the old authenticator entry. This order matters because removing the old method too early can leave me with fewer options.
A lost phone creates two separate concerns: access to the online account and access to the authenticator app. The account’s recovery tools address the first concern, while the PIN or biometric protection helps reduce casual access to the second. I would contact the mobile carrier or use the device-maker’s security tools where appropriate, but I would not assume that remotely securing the phone automatically transfers the authenticator entries to a replacement device.
When a phone is reset, I would expect to repeat account setup unless I have a documented recovery route supported by each individual service. That is why I consider recovery codes and setup records part of the initial configuration, not optional paperwork. The most secure workflow is not merely “turn on two-factor authentication”; it is “turn it on and know how to recover without weakening the account.”
There is a useful distinction between an app problem and an account problem. If SafeAuth opens, displays the relevant entry, and produces changing codes, the account may be rejecting the configuration, the clock may be out of sync, or the service may be experiencing a login issue. If the app itself will not open or the local lock cannot be passed, the phone and app installation become more relevant. Separating those situations keeps troubleshooting focused.
When SafeAuth is not the cause
Some failed logins have nothing to do with the authenticator. A service may require a password reset, flag a new device, block a suspicious sign-in, or demand an additional confirmation. In those cases, a valid second-factor code may still be insufficient. I would read the exact message on the login page instead of assuming that generating another code will solve it.
Network problems can also create misleading results. SafeAuth may generate a code locally while the website is unavailable or while the login request is delayed. Repeatedly submitting codes during a slow connection can lead to several expired attempts. Waiting for the service to load normally and then using one fresh code is a better approach than cycling through entries.
It is also worth checking whether the account expects a different authentication method. Some services distinguish between an authenticator code, a text message, an approval prompt, and a security key. Choosing the wrong option on the login screen can make SafeAuth appear ineffective even though it is working exactly as intended.
Compared with text-message verification, an authenticator app is less dependent on cellular delivery and avoids the delays that can affect one-time messages. Compared with a password manager that includes authentication codes, SafeAuth is more narrowly focused. That narrower role can be appealing if I want the second factor kept separate from my passwords, but it also means I may manage more than one security app.
Compared with a hardware security key, SafeAuth is easier to install and does not require carrying another physical object. A hardware key can be a better fit for people protecting highly sensitive accounts or wanting stronger resistance to certain phishing situations. For ordinary personal accounts, SafeAuth offers a more accessible step up from passwords and text messages, as long as I understand that a code can still be entered into a convincing fake login page.
Who will appreciate it, and who should choose differently
I think SafeAuth is a good match for someone moving beyond SMS verification, a person managing several ordinary online accounts, or anyone who wants PIN and biometric protection around authenticator entries. Its straightforward purpose makes it less intimidating than a broad security suite, and the free entry point lowers the barrier to trying app-based two-factor authentication.
I would be more cautious about recommending it as the only security plan for an organization with strict administrative controls, a person who needs hardware-backed authentication, or someone who cannot safely maintain recovery information. In those situations, a managed enterprise solution, a password manager with a carefully planned recovery system, or a physical security key may be more appropriate.
It is also not the right tool for someone expecting automatic account protection. SafeAuth does not replace strong, unique passwords, device security, software updates, or awareness of phishing. The app can protect the second step, but it cannot decide whether a login page is genuine or recover an account when every backup method has been lost.
SafeAuth comes from SafeAuth Services and has built a sizable user base, with more than ten million installs, a 4.4 average from roughly one hundred sixty-one thousand ratings, and about two thousand written reviews. Those figures suggest that the app is familiar to many Android users, but popularity should not replace a careful setup. I pay more attention to whether the workflow fits my accounts and whether I can maintain recovery access.
My practical verdict after using it
My overall impression is positive, with one important condition: SafeAuth rewards preparation. The app is easy to understand once an account is connected, and its PIN and biometric protection give the authenticator a useful privacy boundary. The real friction happens around the app—clock synchronization, QR-code handling, account labels, recovery codes, and knowing which service controls the login.
I would install it for personal accounts where I want to move away from text-message codes without adopting a more elaborate security setup. I would label every entry clearly, test each account before closing its security settings, store recovery information securely, and keep a replacement-phone plan. Those steps make a much bigger difference than repeatedly reinstalling the app whenever a login fails.
The free price makes experimentation easy, while the presence of optional purchases means I would read any payment prompt rather than assuming it is necessary. The Everyone rating and Android six minimum also make it approachable for a broad range of users. Still, the app’s value depends on disciplined account management, not just installation.
My recommendation is to use SafeAuth when you want a focused, protected home for verification codes and are willing to handle recovery responsibly. It is not a complete account-security strategy, and it is not a substitute for a hardware key in every high-risk situation. For everyday Android users who want a practical authenticator with an extra local lock, though, it is a sensible option—as long as the setup is treated as carefully as the login it is meant to protect.
Authenticator App - SafeAuth FAQ
What is Authenticator App - SafeAuth used for?
Authenticator App - SafeAuth is designed to add an extra layer of protection to online accounts through two-factor authentication. After linking a compatible account, it generates temporary verification codes that change regularly. You can enter these codes alongside your password when signing in, helping protect your accounts even if your password has been exposed.
How do I set up an account with Authenticator App - SafeAuth?
Setup normally involves opening the security settings of the service you want to protect and selecting an authenticator-app option. You can then scan the displayed QR code with SafeAuth or enter the setup key manually. Once the account is added, the app begins generating time-based codes. Always confirm the first code before closing the setup page.
Can SafeAuth work without an internet connection?
In most cases, authenticator codes are generated directly on the device, so an active internet connection is not required when you are signing in. This makes the app useful while traveling or in areas with limited coverage. However, your device’s date and time should be set automatically, because an incorrect clock can cause otherwise valid codes to be rejected.
What happens if I lose my phone or change devices?
Losing access to your phone can make two-factor authentication accounts difficult to recover, depending on the service involved. Before changing devices, use each account’s recovery options, backup codes, or transfer feature if available. SafeAuth should not be treated as the only copy of your security information. Store recovery codes securely and never share them with anyone.
Is Authenticator App - SafeAuth safe to use?
An authenticator app can significantly improve account security because it creates short-lived verification codes rather than relying only on passwords or text messages. Nevertheless, your protection also depends on securing the phone with a strong lock, downloading the app from an official store, and avoiding suspicious links. Keep the application updated and protect any backup or export data carefully.